Node.js SDK
npm install @vulnify/sdk. check(), guard(), and the CLI. Node.js.
Before the action runs
Vulnify is a runtime authorization layer. It does not scan machines or source code for vulnerabilities. It governs what agents and automations can access and do. The web app is app.vulnify.io. The API is https://api.vulnify.io.
Node.js: npm install @vulnify/sdk. Python: pip install vulnify. Create an API key in the app first. The full install is on the quickstart.
check() returns the decision. guard() runs your function only when that decision is ALLOW. Run the export, send, or delete only after ALLOW.
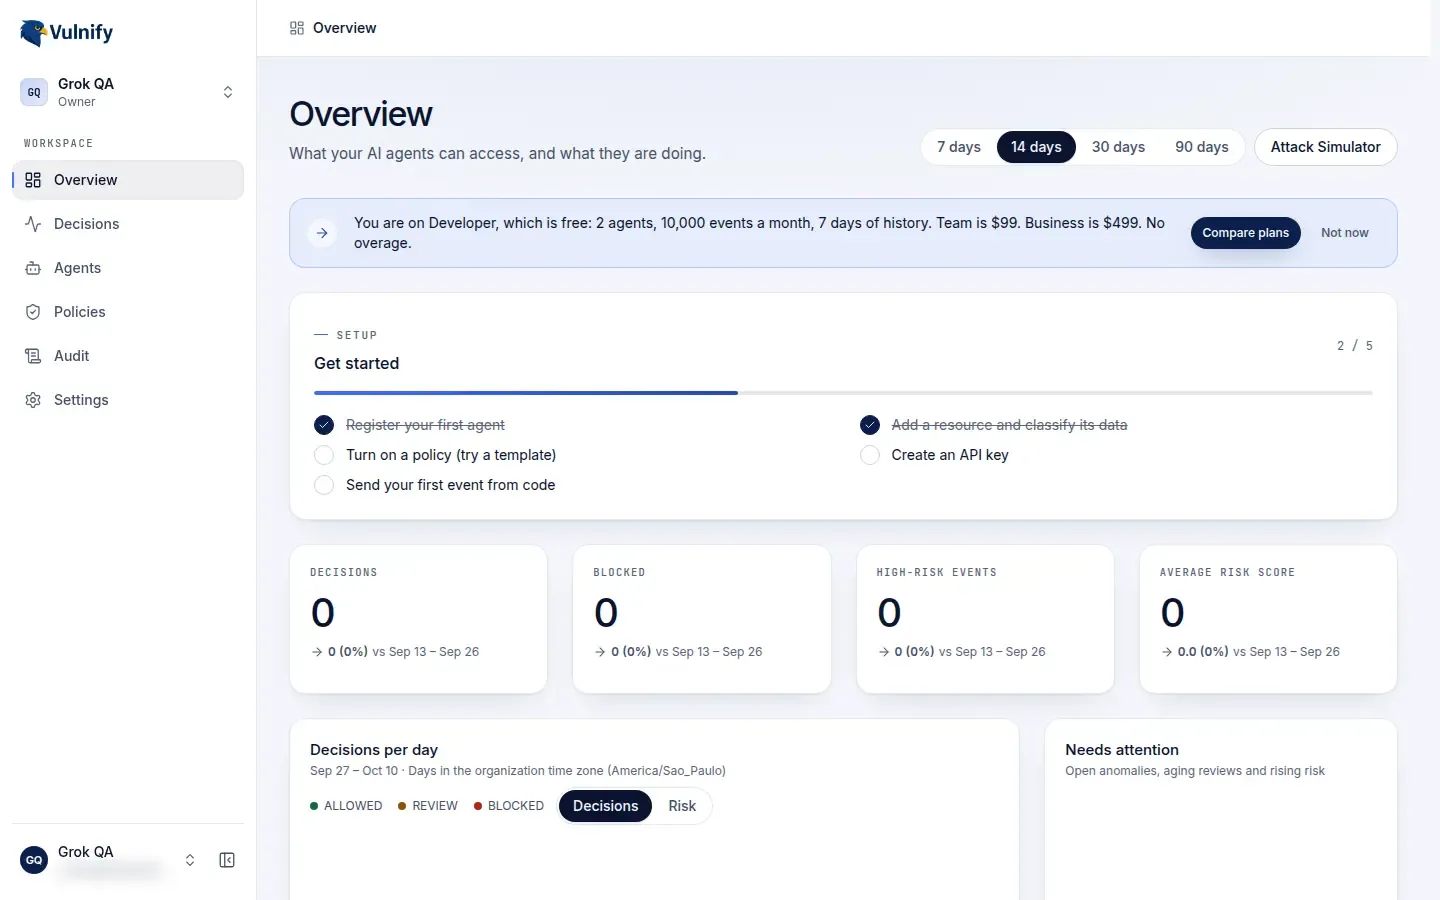
Open the event in app.vulnify.io. The overview counts live decisions. A TEST key stays in the sandbox and out of those charts.
const decision = await vulnify.check({  agent: 'SalesBot',  action: 'EXPORT_DATA',  resource: 'Customer Database',  destination: 'EXTERNAL_EMAIL',  recordsAffected: 12000,});
if (decision.finalDecision === 'ALLOW') {  await exportCustomerRecords();}
guard() is the shorter form. It throws for REVIEW and BLOCK. Both SDKs are on Node.js and Python.
Node.js SDK
npm install @vulnify/sdk. check(), guard(), and the CLI. Node.js.
Python SDK
pip install vulnify. The same decision, with final_decision. Python.
Policies
Rules that allow, send to review, or block, in enforce or monitor mode. Policies.
Monitor mode
Record what would have been blocked or reviewed, and answer ALLOW. Monitor mode.
Audit log
A per-organization SHA-256 hash chain, and Verify audit chain in the app. Audit log.
Slack approvals
Approve or Deny a review from the alert. Slack.
Vulnify MCP server
Sign in with Vulnify from Claude, Cursor, or Grok. Separate from the MCP gateway. Vulnify MCP server.
API reference
POST /v1/events and the rest of the machine contract. API reference.
A check sends action metadata: the agent, the action, the resource, the destination, and how many records are affected. Vulnify is designed to store that metadata, not the contents of your records.
You can optionally send content so the server can scan it for sensitive data. Matches come back as findings. The content itself is not stored. See Risk engine.
| Decision | What you do |
|---|---|
ALLOW |
Run the action. |
REVIEW |
Do not run the action. A person has to approve it, for example in Slack. |
BLOCK |
Do not run the action. |
In monitor mode the event is stored and not enforced. Follow finalDecision. evaluatedDecision is what enforcement would have returned. If Vulnify cannot be reached, the SDKs fail closed by default and return BLOCK. A rejected request, including a body over 200 KB, throws instead. See Decisions.
Two ways to ask. Check, then act: your code calls the API or an SDK, and runs the tool only after ALLOW. Gateway: the app can register an HTTP API or an upstream MCP server as a route. Callers send the call to Vulnify. Vulnify decides, and forwards it to that upstream only when the decision allows it. The MCP gateway is that path for MCP tool calls. The Vulnify MCP server is a different host: tools for Cursor, Claude, and VS Code. The app describes the gateway path as beta. A credential for the upstream is injected only after ALLOW, and the agent never sees it.